Wingman AI
A live data graph of your security programme. A continuously-updated brief that tells you what it means. Wingman maintains it around the clock. You make the decisions.
Two parts that make this work
The graph is the data: incidents, vulnerabilities, threats, risks, assets, controls, requirements, plans and tasks — connected by their real relationships. A vulnerability comes in and the suggestions for the links between affected assets, controls, owners and requirements are created. Nothing to cross-reference by hand.
The brief is the insight: a continuously-updated description of your programme — kept on every entity, refreshed when the underlying facts change, rolled up to the whole. Written in prose your CFO, your board, and a new hire on the security team can actually read. Audit packages, customer questionnaires and board updates are extracts from the brief — not separate documents you keep current on the side.
Wingman runs on its own clock: always scanning, always updating, surfacing what's drifting. Wingman keeps the watch. You make decisions.
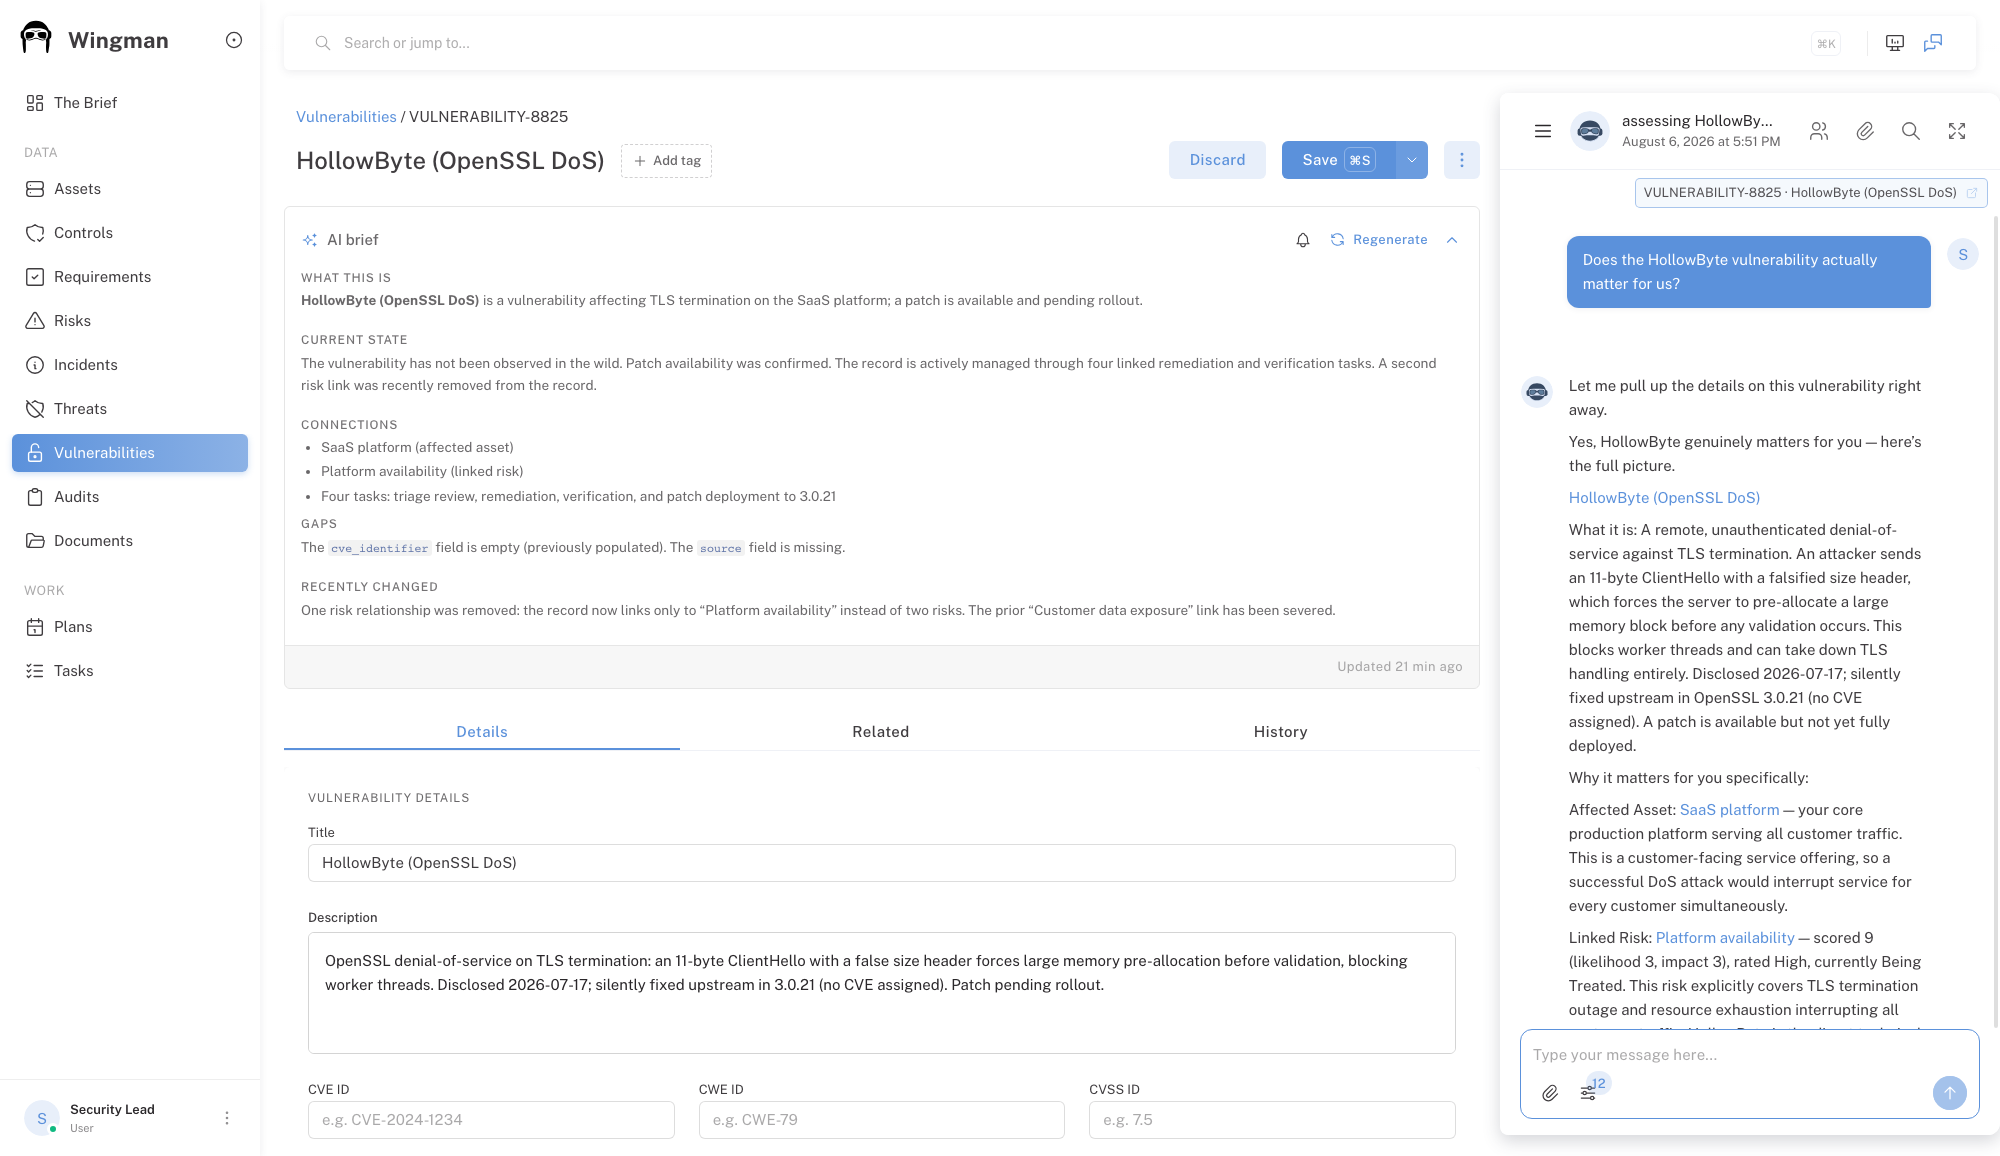
From finding to decision in minutes, not hours
Your scanner flags a vulnerability. Now what? You check which assets are affected, whether there's a control that covers it, who owns the remediation, and whether it maps to any compliance requirement. That cross-referencing takes 2–4 hours — and it happens every time.
The graph already holds those connections. When a vulnerability comes in, Wingman shows what's affected, who owns it, and whether it actually matters — in 15–30 minutes.
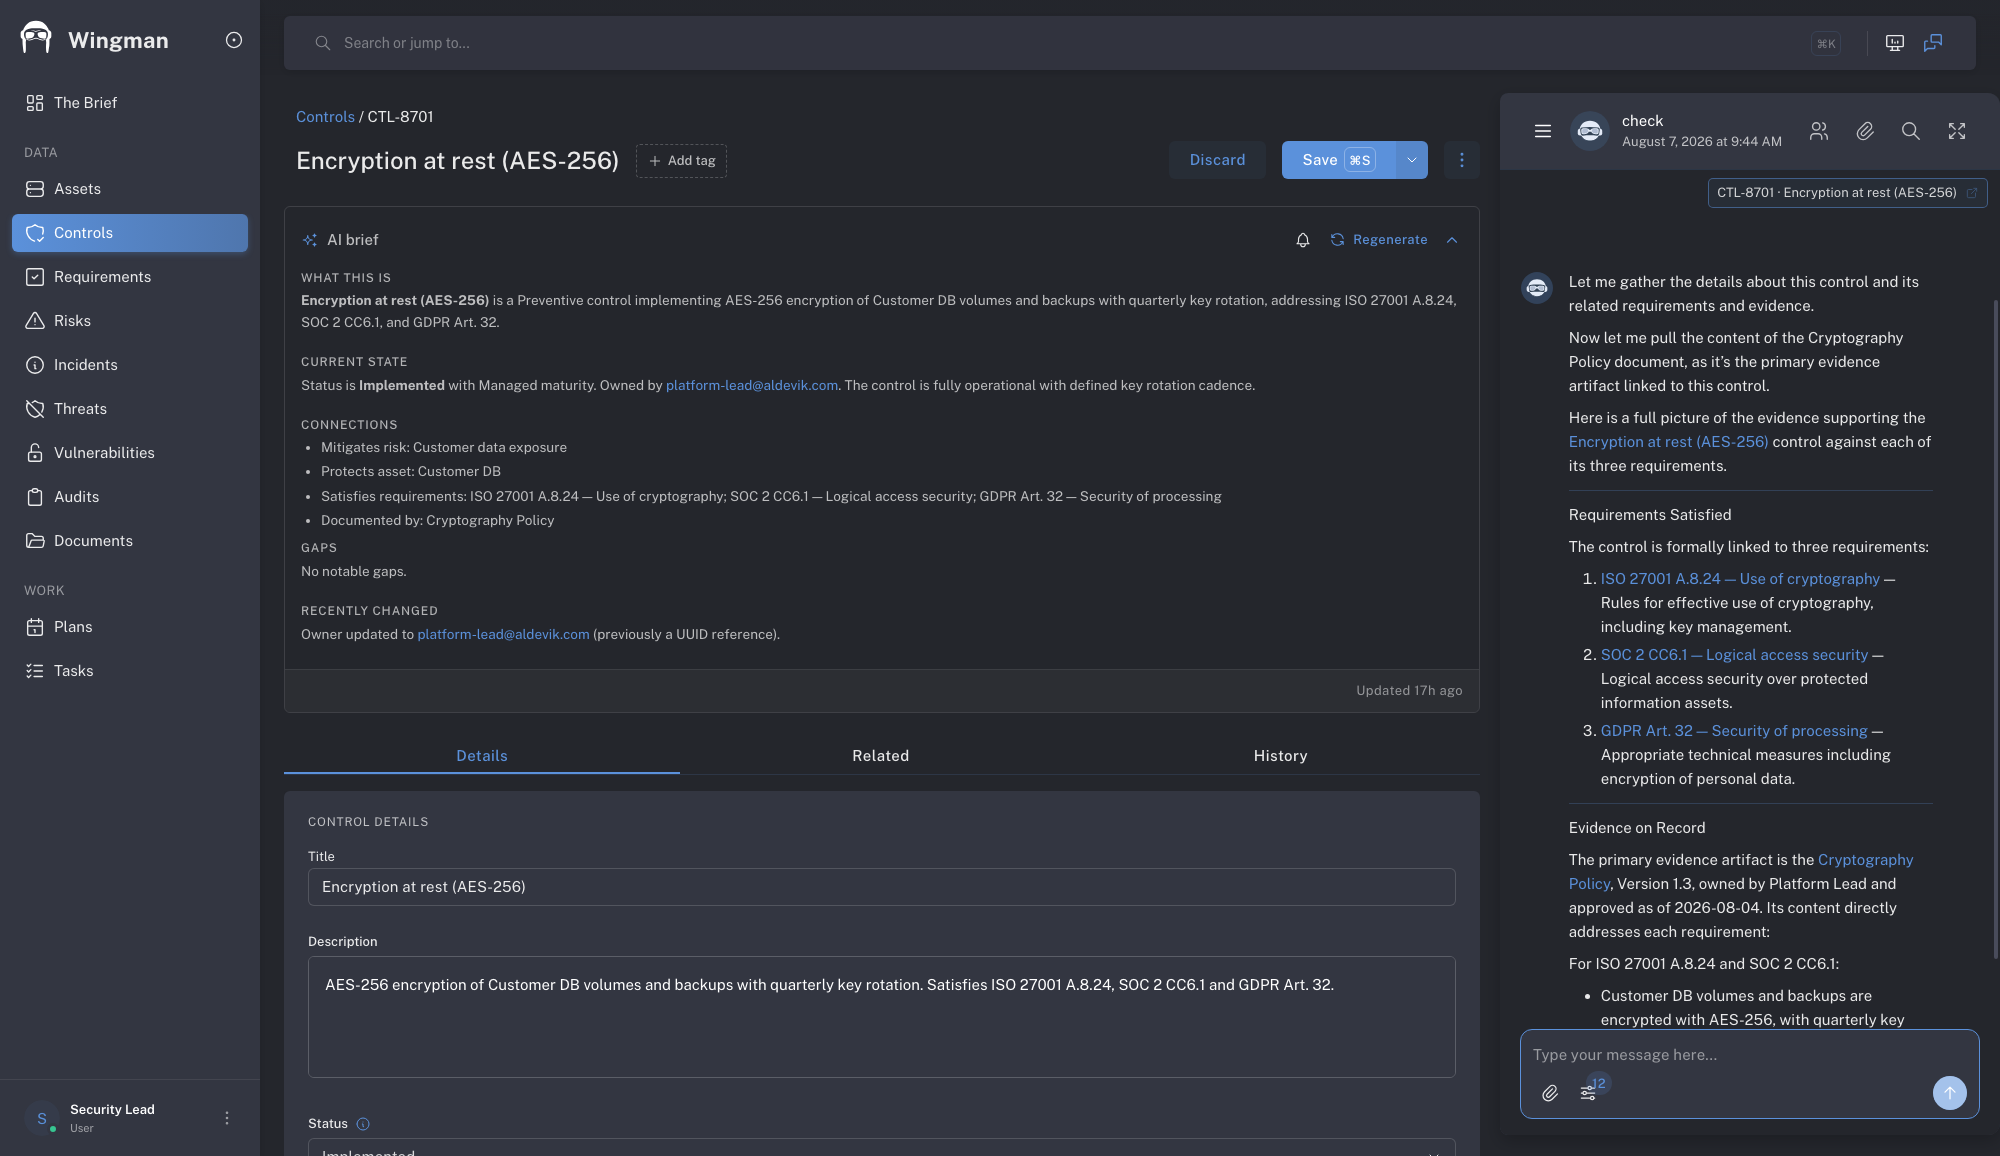
Compliance evidence, collected all year
Every Q4: 150 assets to review, evidence to chase from six different systems, documentation to update before the auditor shows up. Three months of work compressed into six stressful weeks.
Wingman helps to collect evidence continuously and distributes reviews throughout the year. By the time the auditor arrives, the package is already built. When they ask for access review logs from Q2, you already have them.
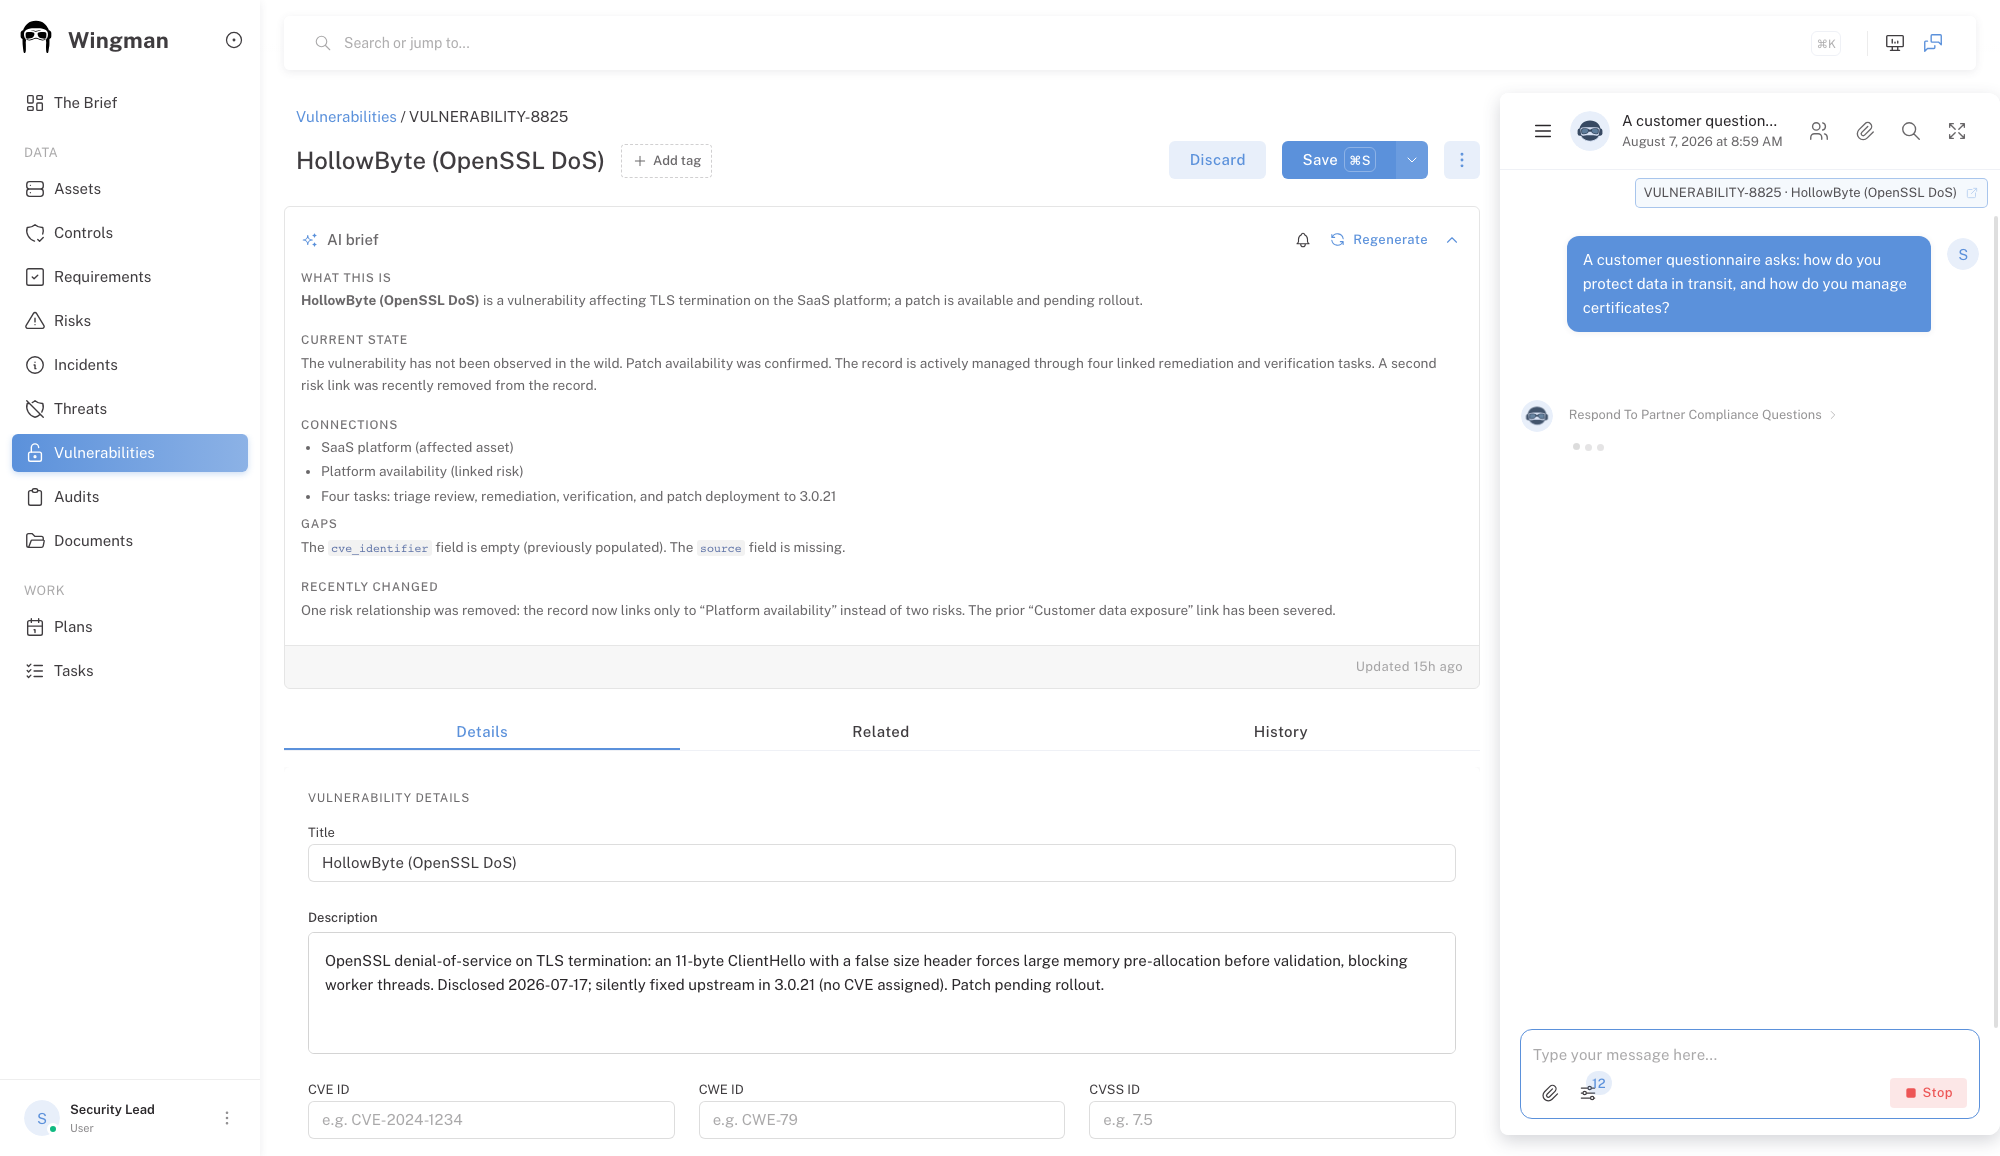
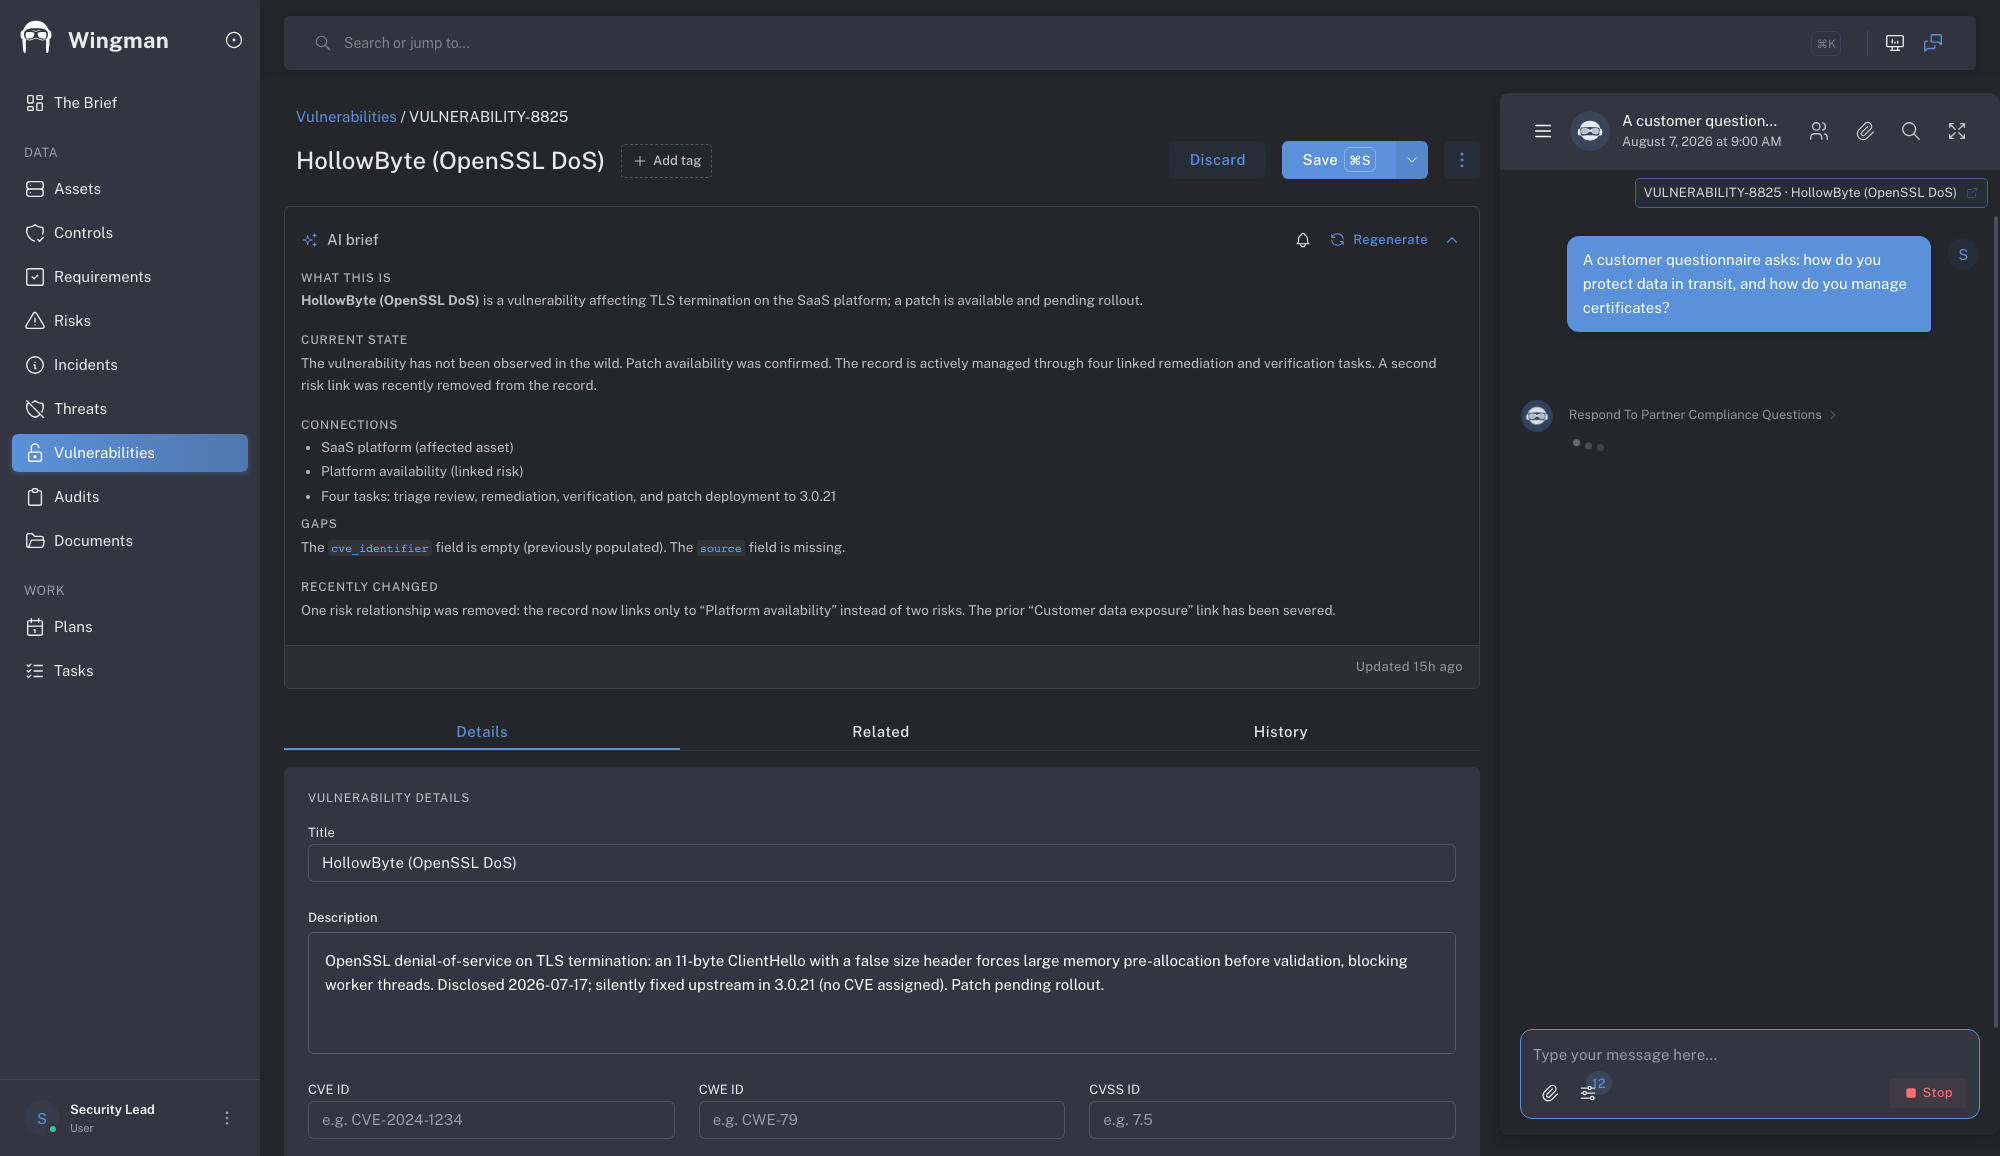
Customer questionnaires in 30 minutes, not 3 days
A prospect sends a 40-question security questionnaire. Someone has to hunt through policies, dig up the factsheet, and write answers that are accurate as of today — not six months ago. This can take days and happens all the time.
Wingman pulls answers from your live asset graph and control library. You review and send. The whole thing takes 30 minutes — and the answers reflect your actual current posture, not whatever was in the last policy document.
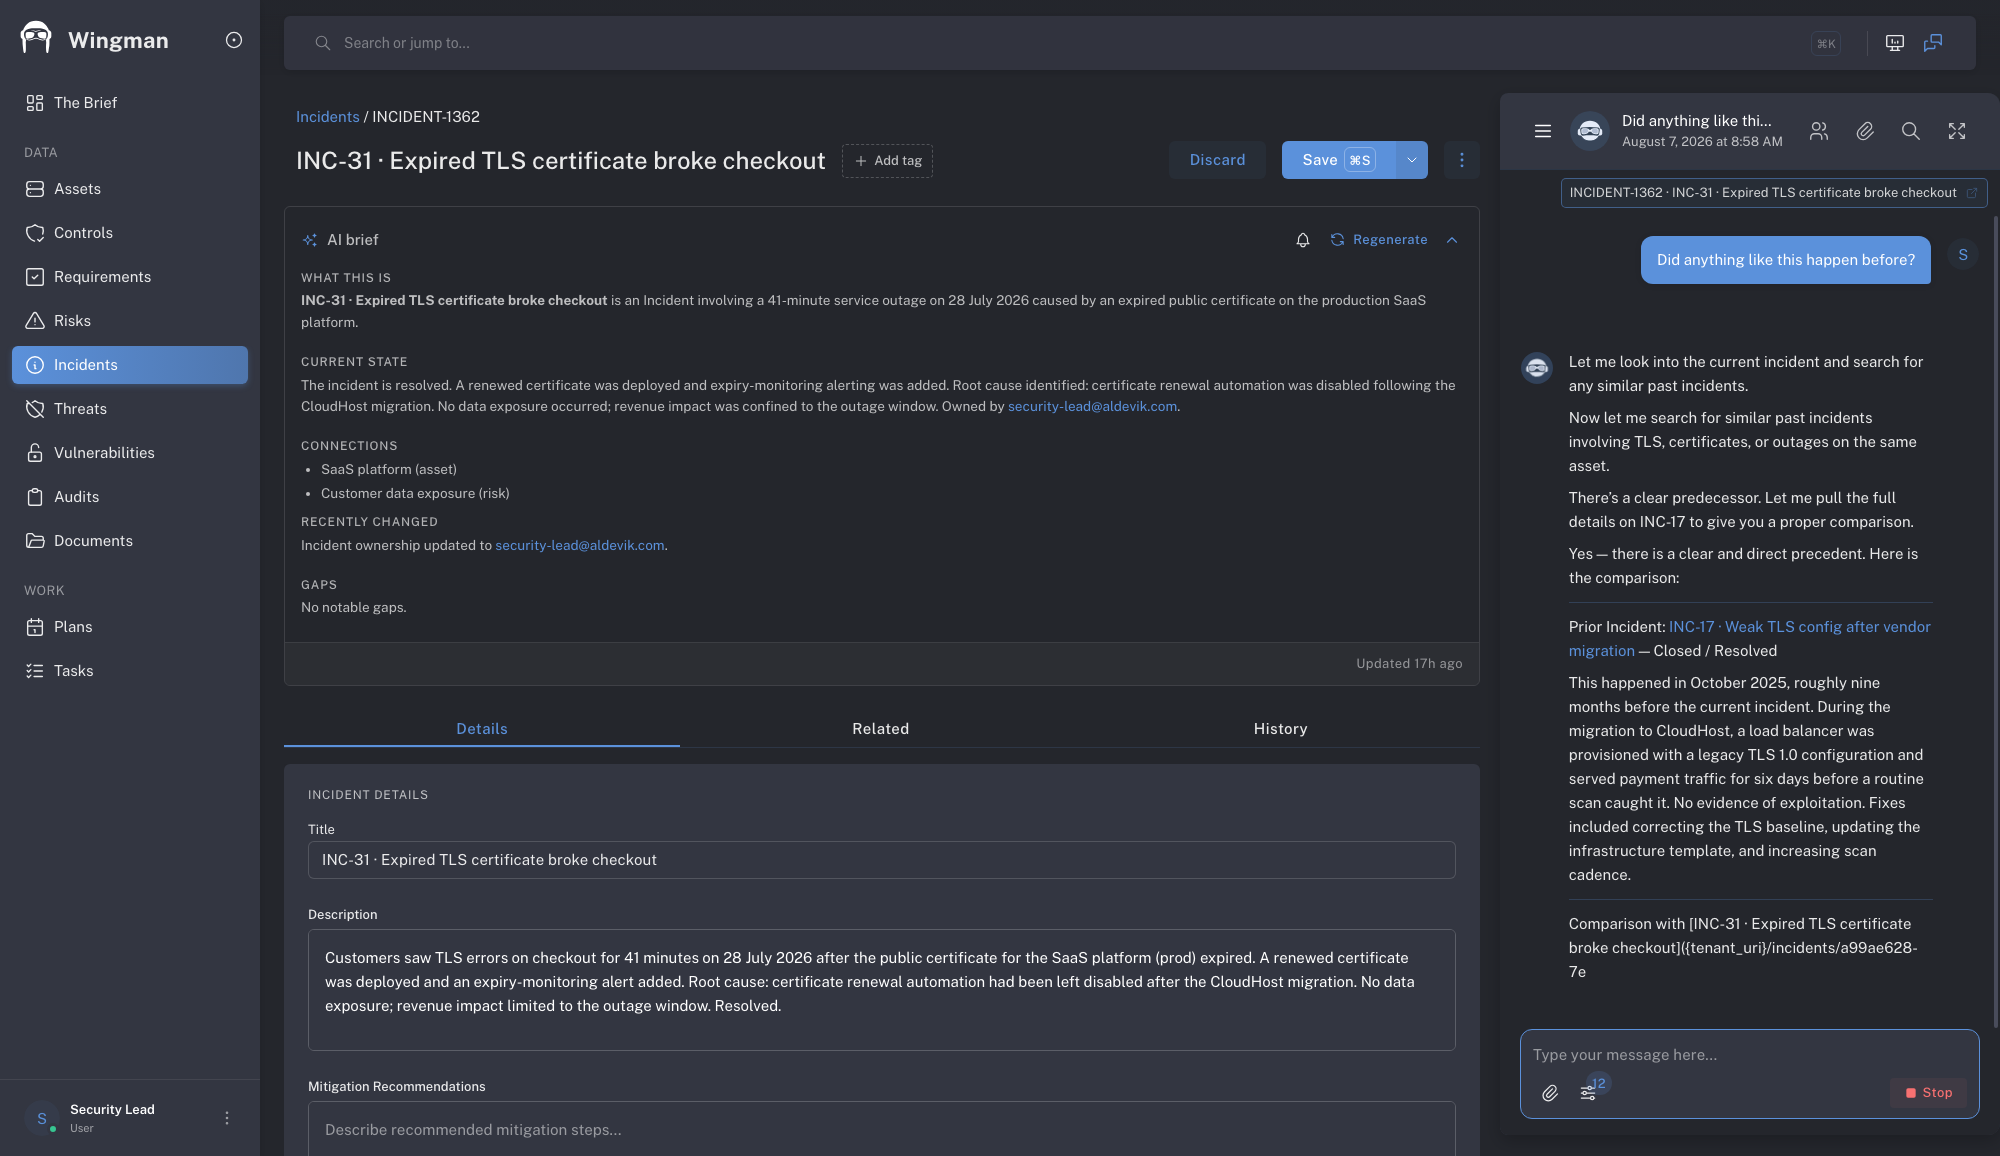
Incident response with context, not guesswork
Something goes wrong at 2am. You need to know what's affected, what controls apply, what decisions were made the last time something similar happened, and who needs to be in the loop. Figuring all that out takes 3–5 hours — while the incident is still active.
Wingman surfaces the relevant assets, controls, and incident history in one place. Your team can classify, contain, and communicate in 30–45 minutes instead of one and a half workdays.
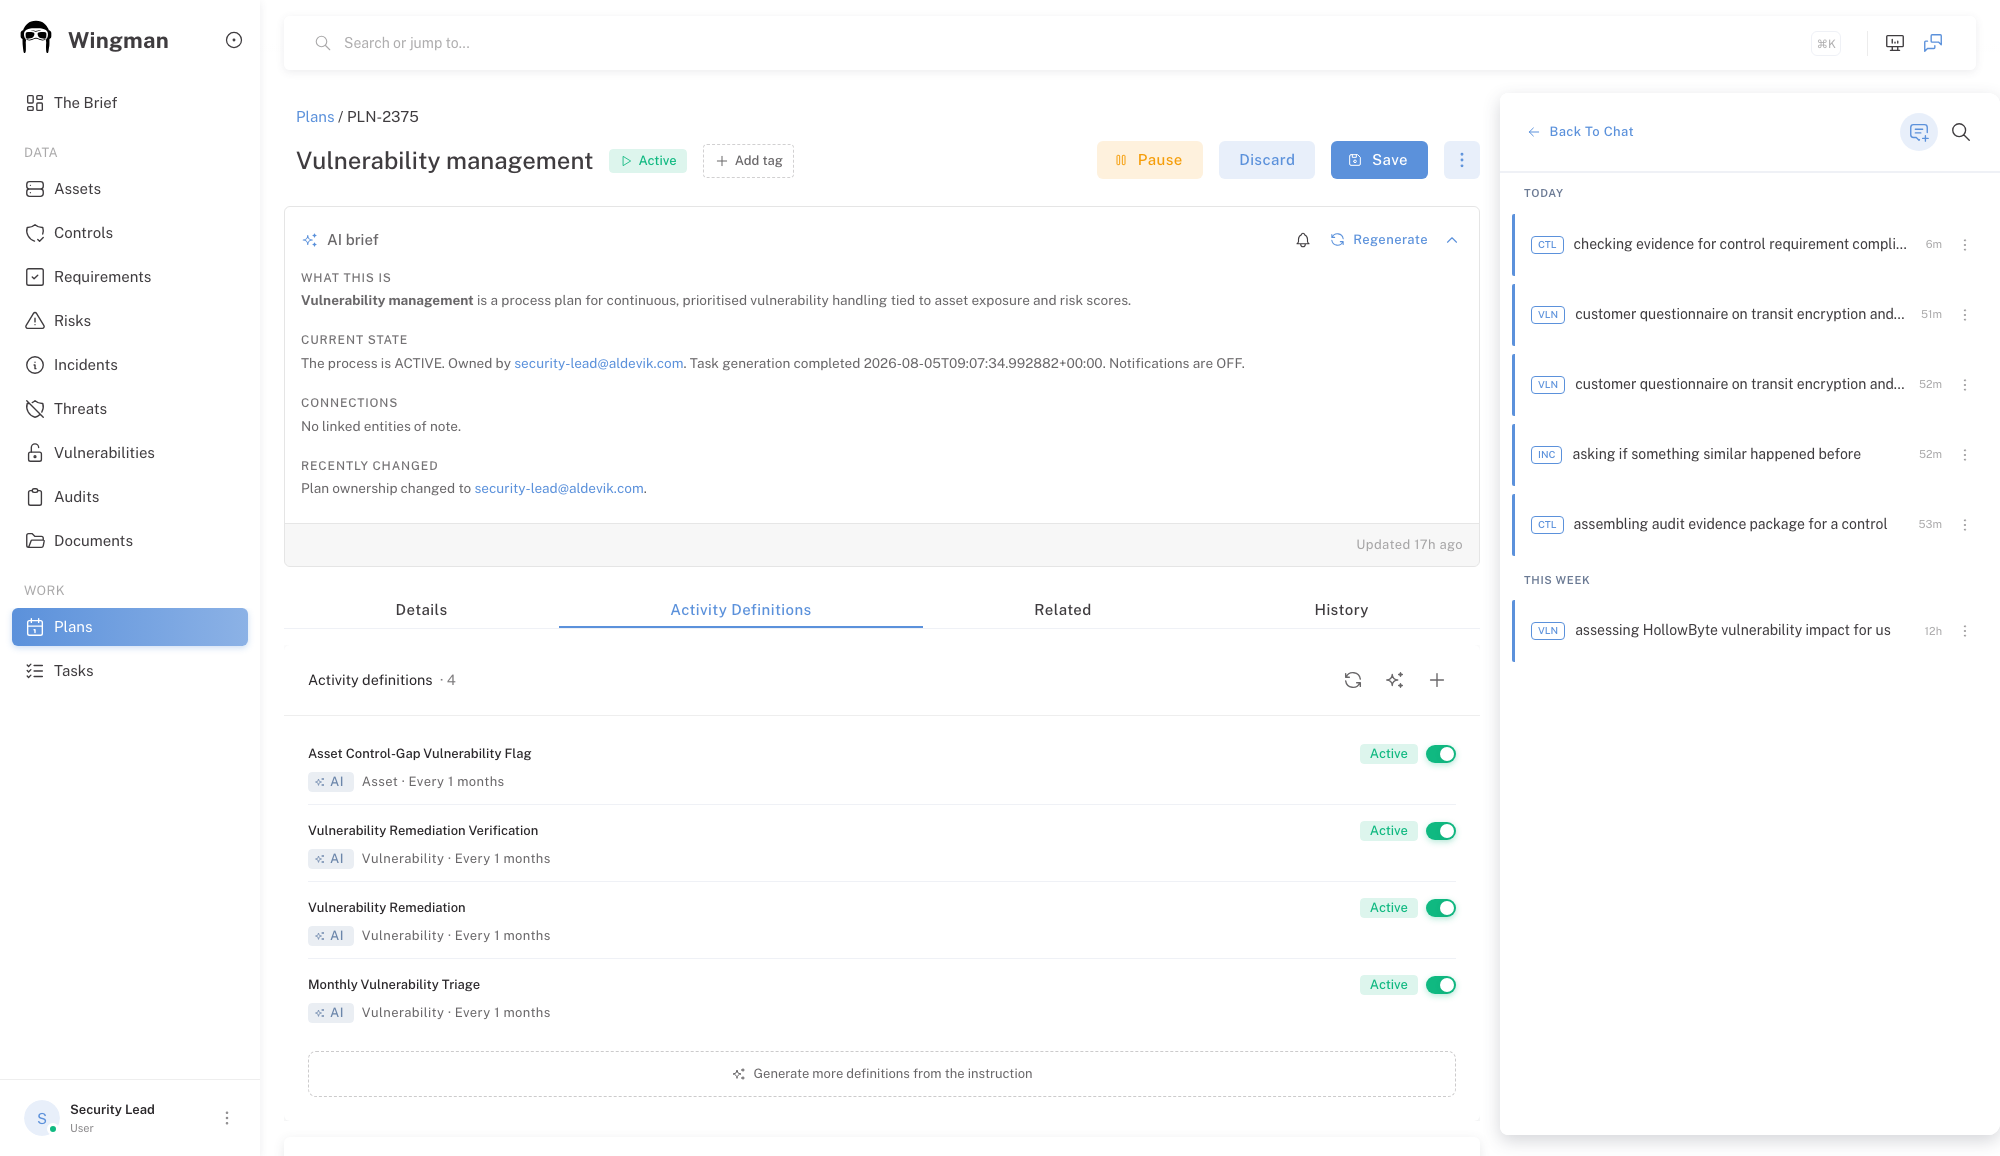
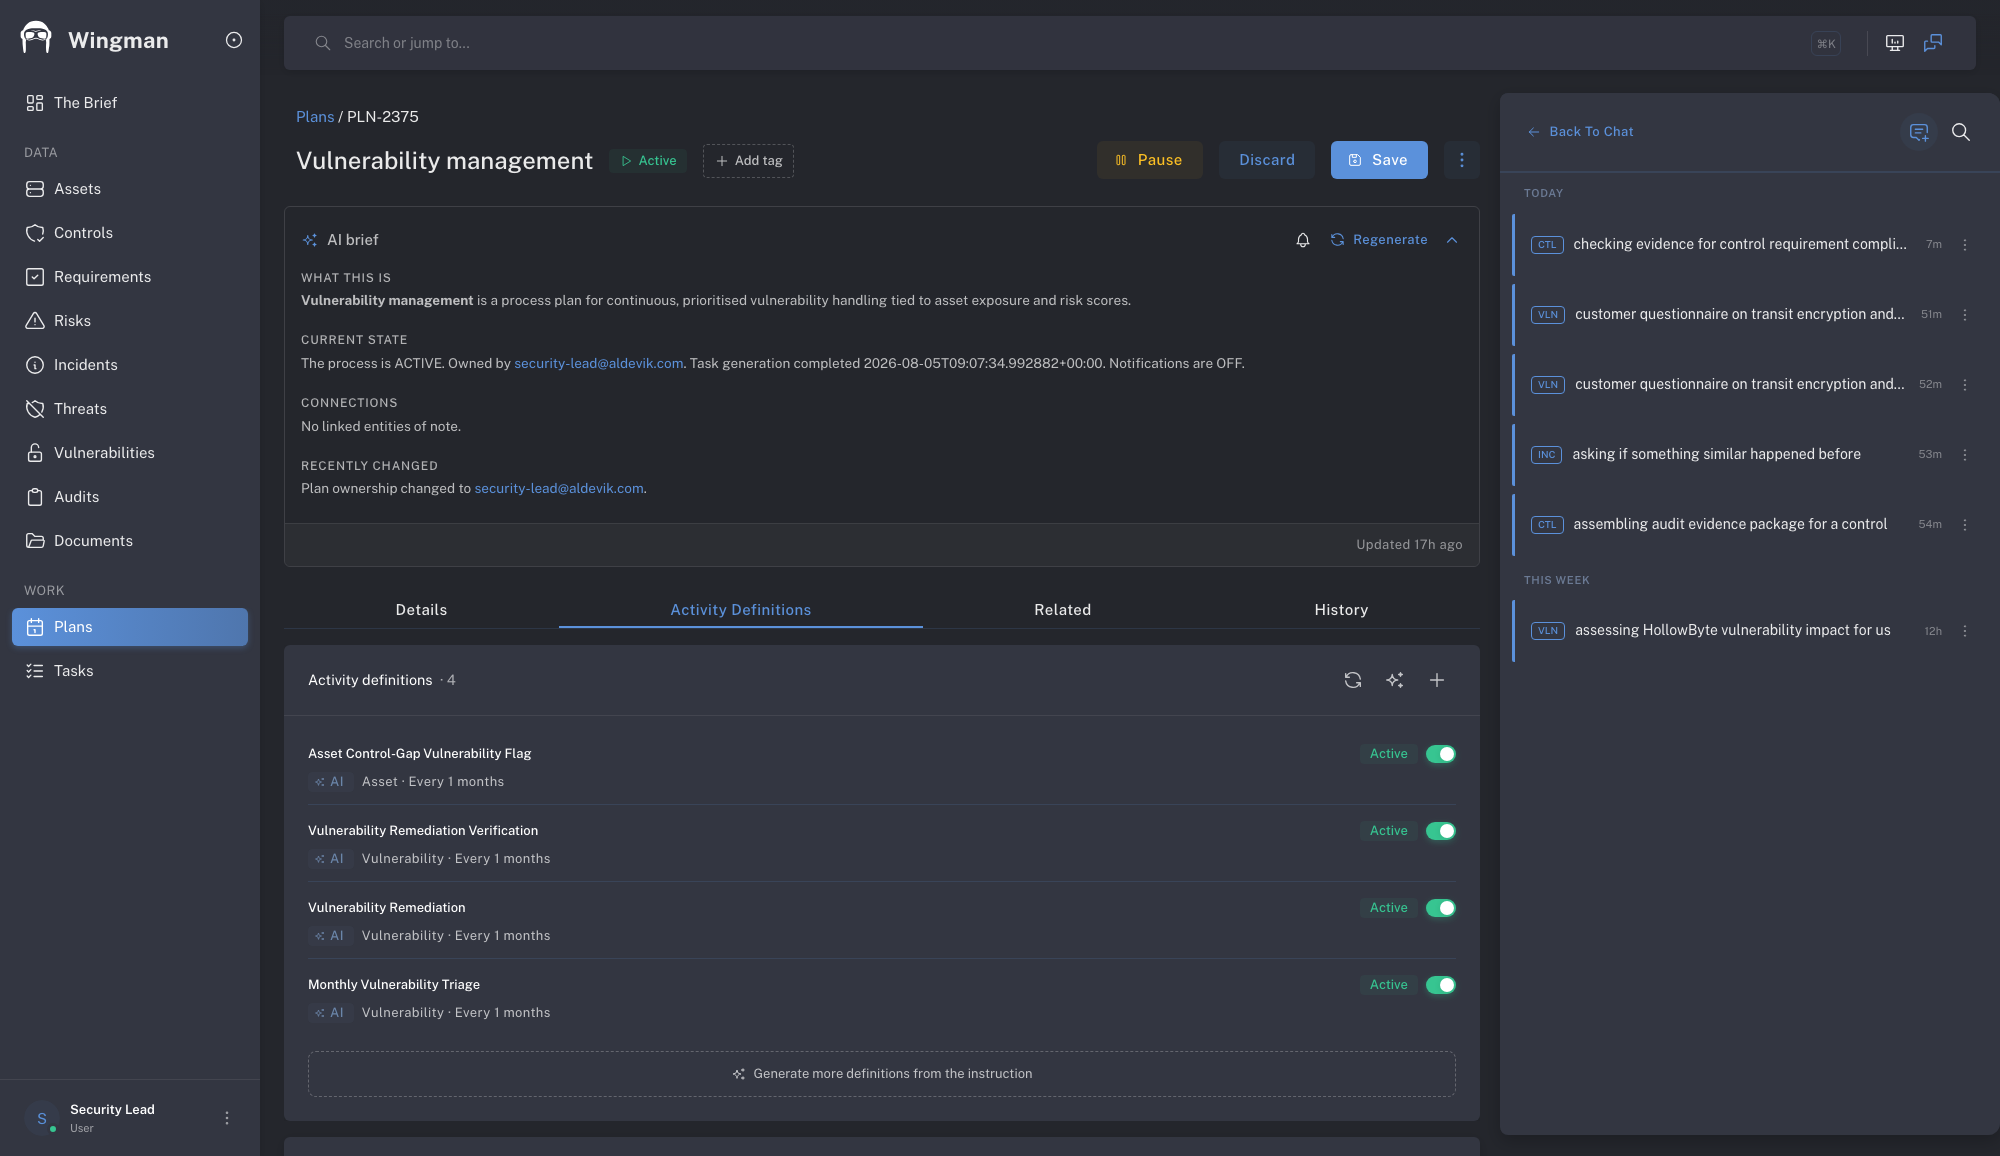
The work, distributed — tasks with context
Finding the problem is half the job. Someone still has to fix it — and "security is everyone's responsibility" has never made that happen.
Wingman turns findings into plans and tasks: a concrete action, assigned to a specific person, with the reason it matters and what done looks like. Reviews are distributed through the year instead of piling up before the audit, and the brief shows what's moving and what's stuck.
Works with your tools
Wingman connects to the systems your team already uses — ticketing, vulnerability scanner findings via webhooks, bulk import from spreadsheets and existing registers, and an MCP interface so your own AI tools can read the programme. You don't replace your stack; you get a layer that ties it together and keeps the security picture current.
Multi-framework without work duplication
If you're running ISO 27001 alongside NIS2 or SOC 2, most of your controls overlap. Wingman treats each framework as a lens on the same programme: one control, one evidence trail, many views. A single control satisfies requirements across frameworks — so you're not maintaining three separate evidence trails for the same thing.
How you can get there
At your own pace, with our team and Wingman's AI alongside yours. Starting from nothing? Wingman suggests assets, risks and a control set from your context and objectives — you confirm what's true and correct what isn't. Already have a programme in spreadsheets, documents and tools? The AI migration assistant onboards it, asking the right questions as it goes. Either way the brief goes live from day one — and it only gets deeper as the programme runs.